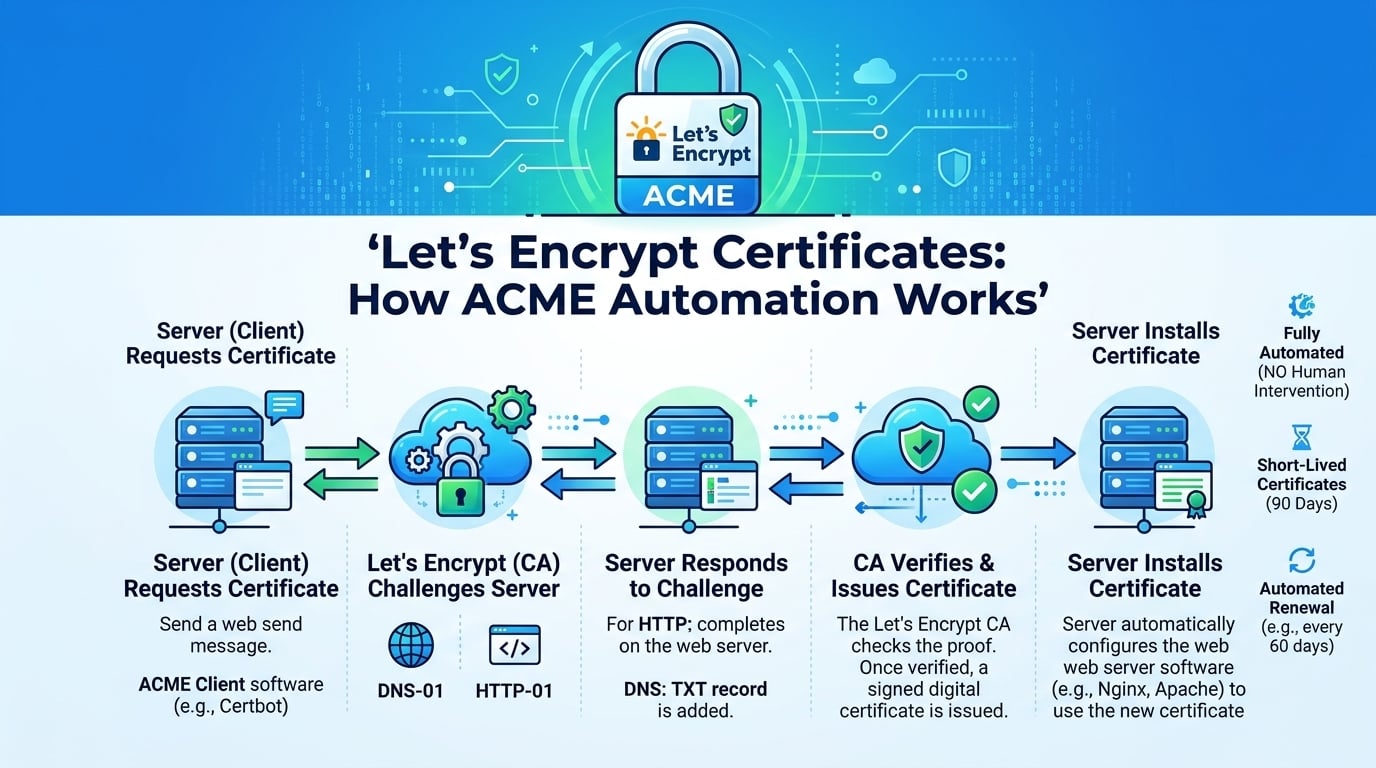
Let's Encrypt Certificates: How ACME Automation Works
A Let's Encrypt certificate is a free, domain-validated X.509 certificate that an ACME client requests, proves control ...
Security - Encryption & Access | CDN Blog | About Content Delivery Network
A Let's Encrypt certificate is a free, domain-validated X.509 certificate that an ACME client requests, proves control ...
OCSP stapling moves the certificate revocation check off the client. The web server fetches a signed OCSP (Online ...
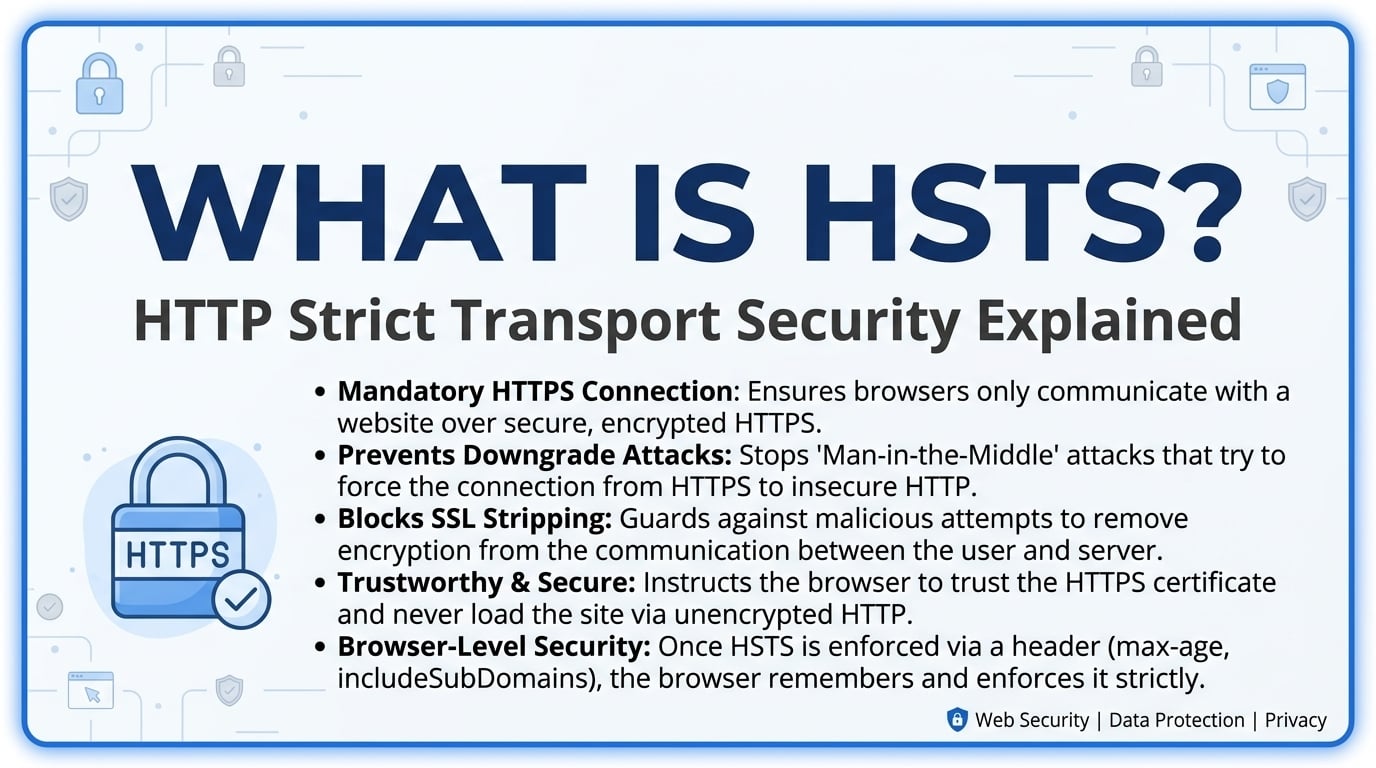
HSTS (HTTP Strict Transport Security) is a response header, Strict-Transport-Security, that tells a browser to contact ...
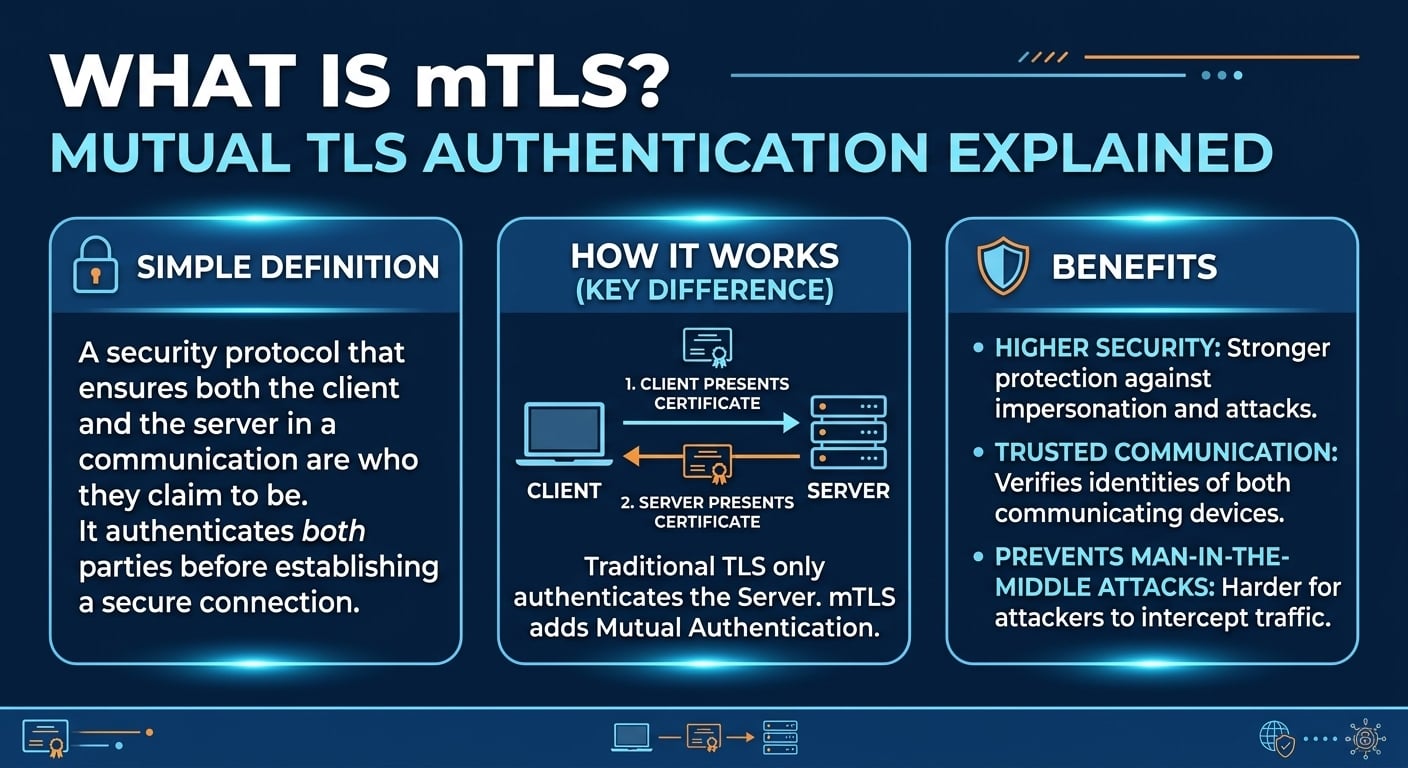
mTLS (mutual TLS) is a TLS mode in which both endpoints prove their identity with X.509 certificates: the server ...
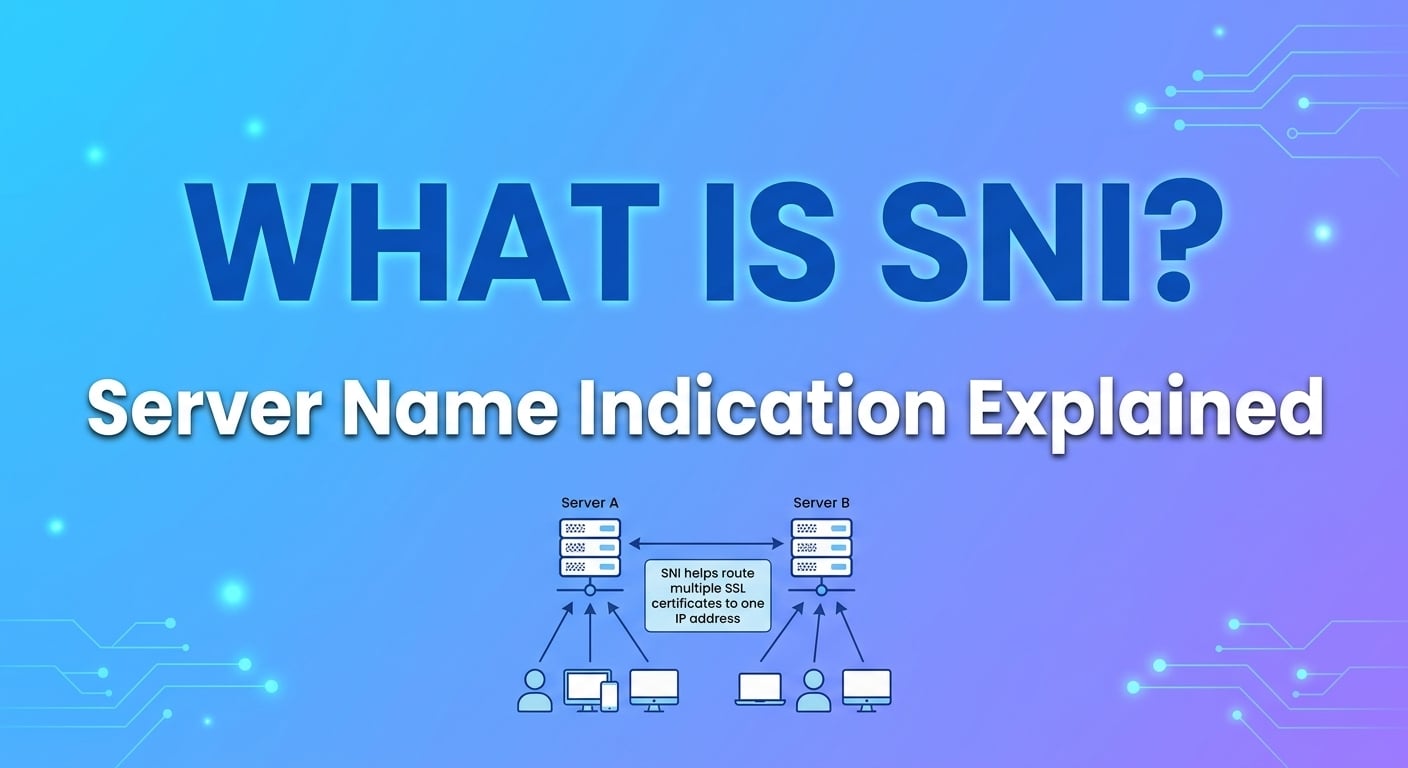
Server name indication (SNI) is a TLS extension in which the client writes the hostname it wants, such as ...
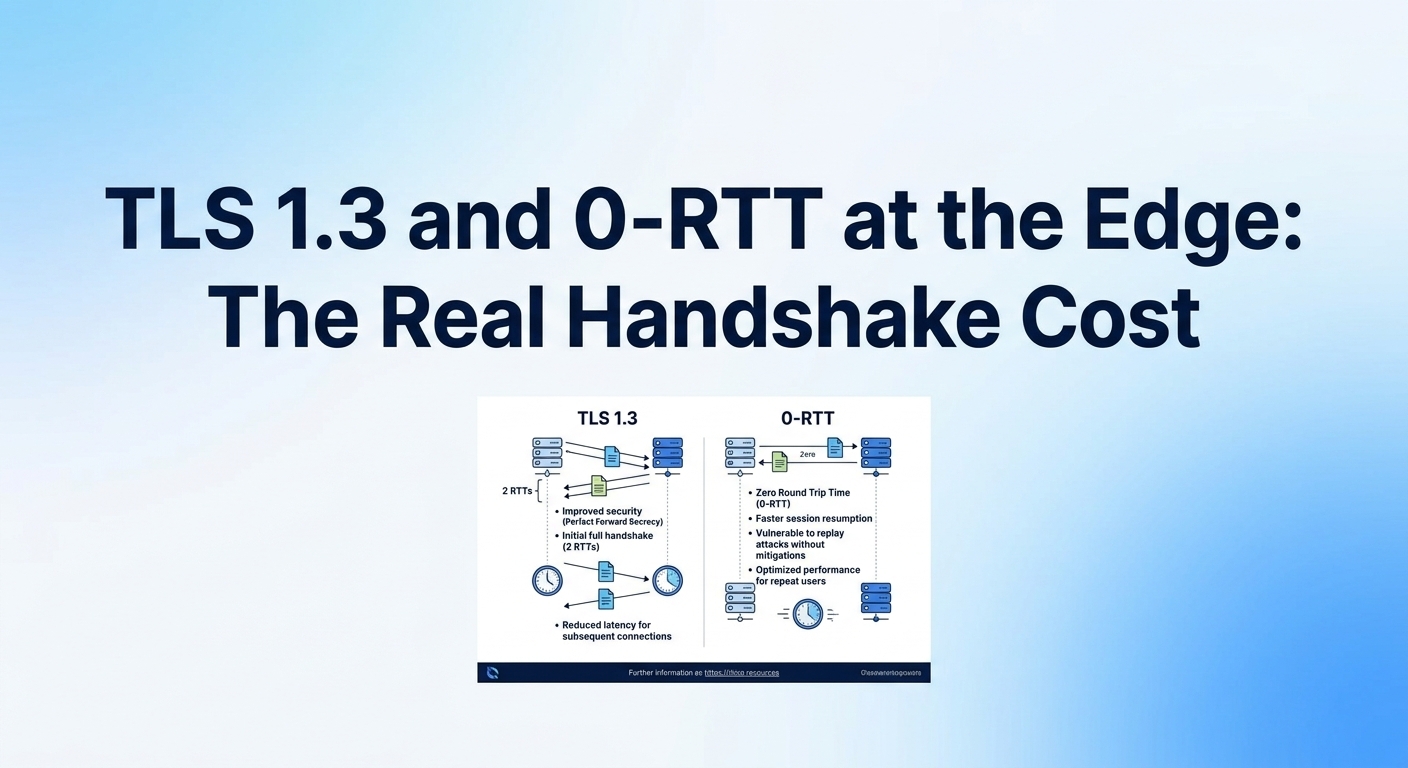
TLS 1.3 removes exactly one round trip from a full handshake compared with TLS 1.2, and 0-RTT removes one more on ...
CDN Signed URLs & Token Authentication: 2026 Playbook A CDN signed URL is a request URL carrying an expiry ...

Google Cloud CDN Setup 2026: The Production Playbook The most expensive line in a Google Cloud CDN bill is rarely the ...
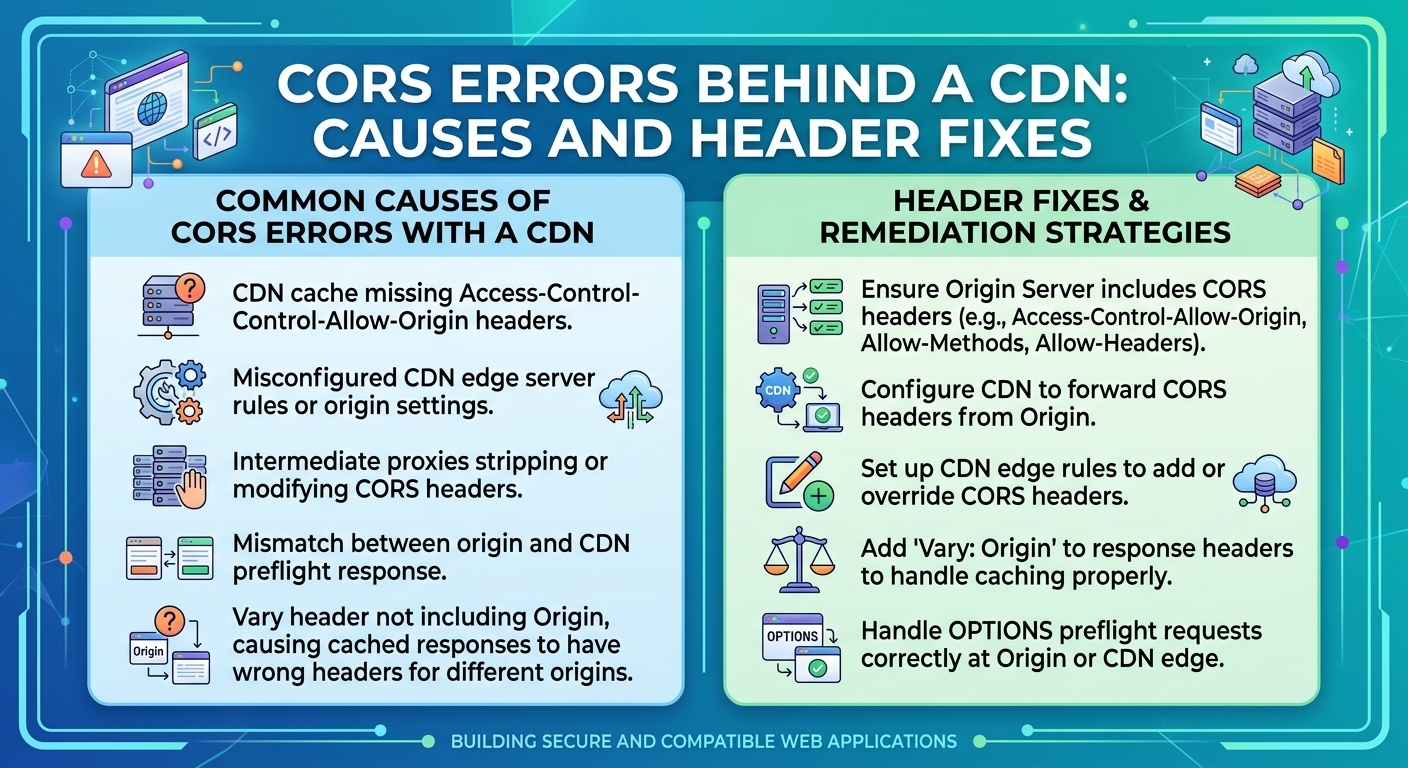
A CORS error behind a CDN is almost never a browser bug and almost never an origin bug. It is a cache key problem. The ...
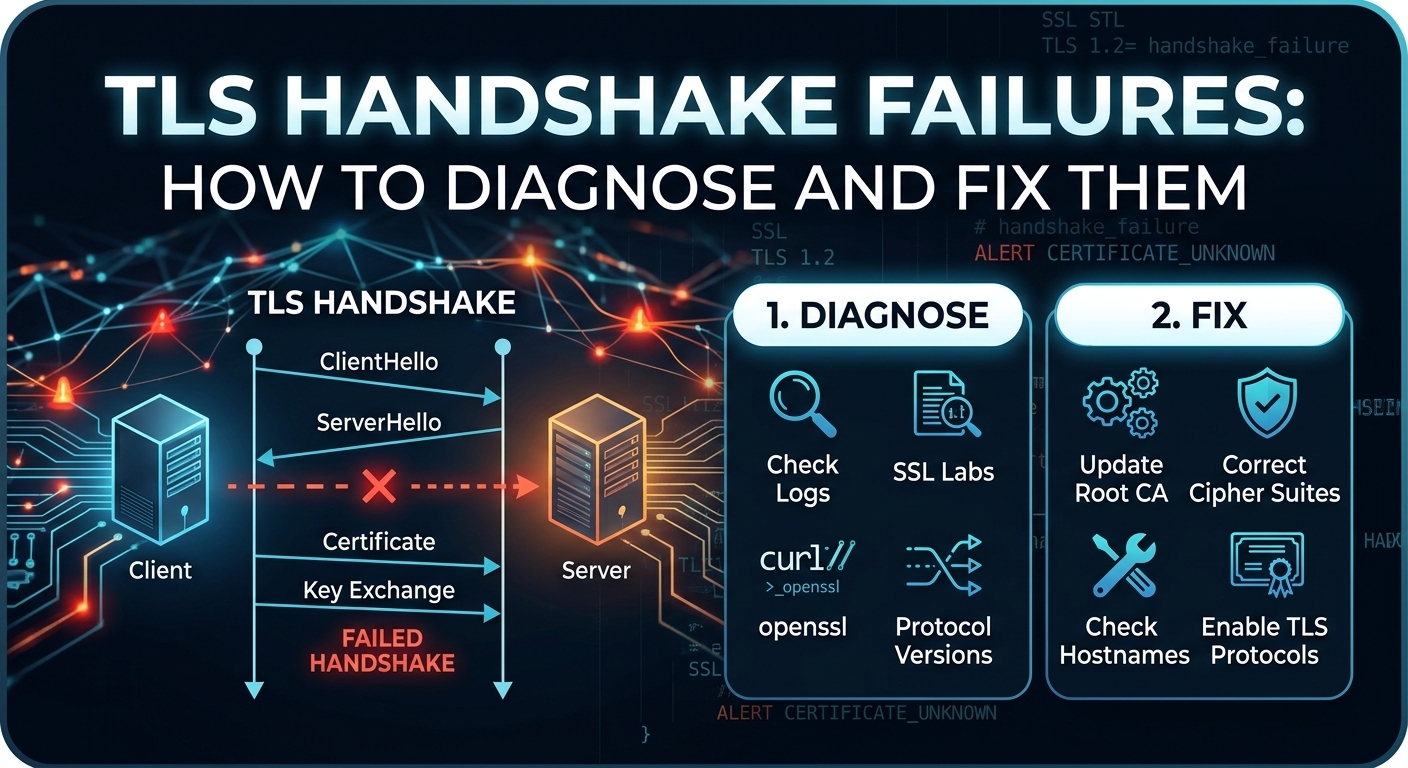
A failed TLS handshake is almost always one of seven things, and you can identify which one in roughly 20 minutes per ...