Learn
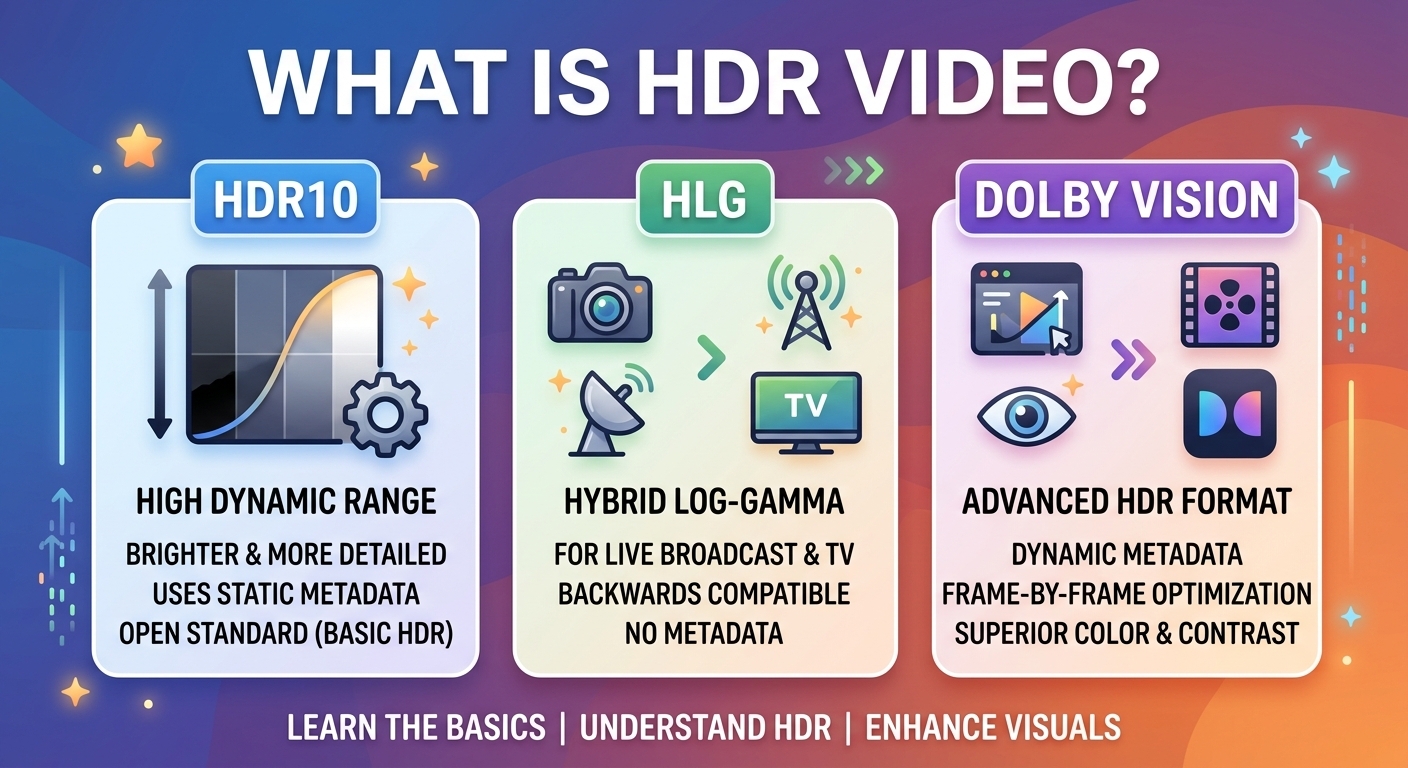
What Is HDR Video? HDR10, HLG and Dolby Vision Basics
The precise answer to what is HDR video: high dynamic range video is video encoded with 10-bit or higher samples, ITU-R ...
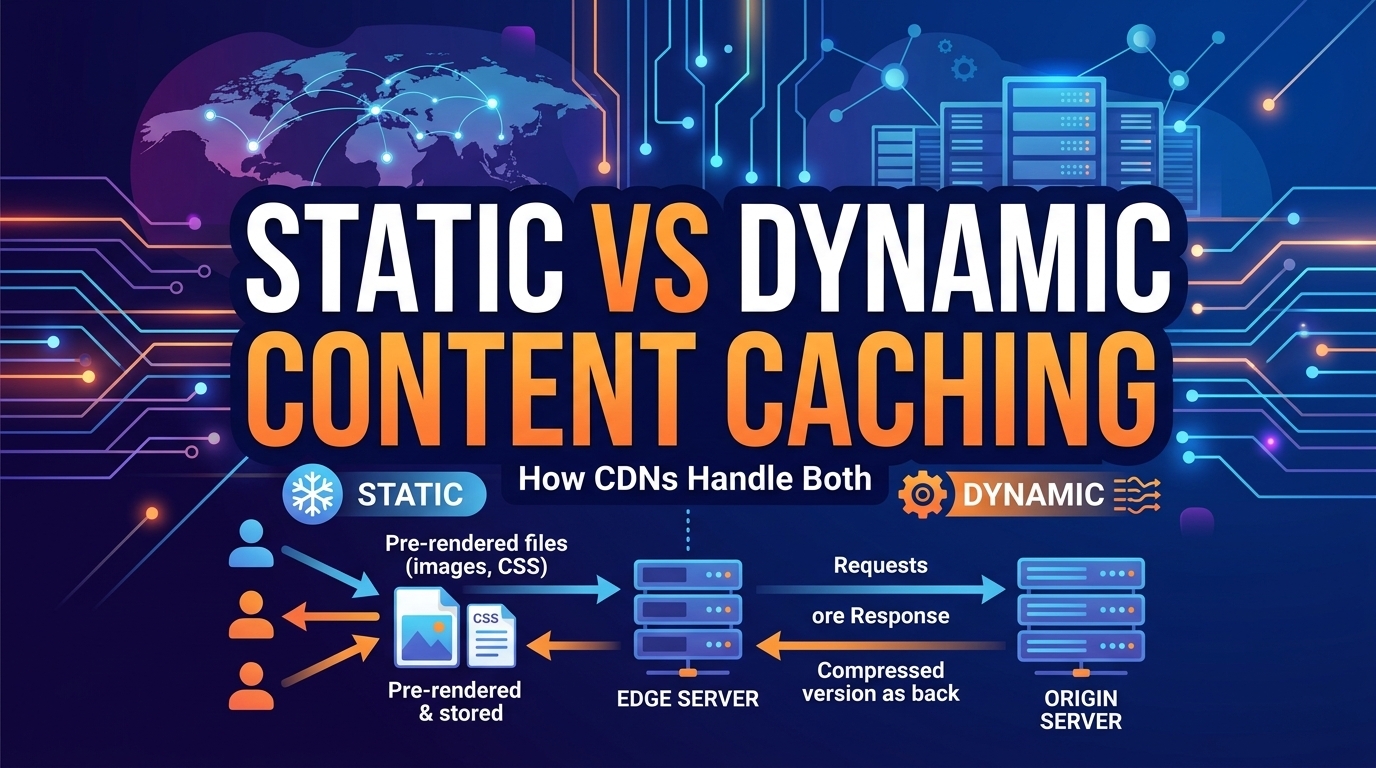
Static assets get year-long TTLs. Dynamic responses get 1 to 60 seconds, and most of the remaining origin savings sit inside that short window. Dynamic content caching means storing responses that change often or vary by user for seconds rather than days, keyed on exactly the inputs that change the output, and serving them stale while the edge revalidates in the background. This article covers four things as of October 2026: the micro-caching arithmetic, cache key patterns for personalized pages, a static vs dynamic decision table, and a failure-mode checklist.
Micro-caching math, as of 2026: put a 1-second shared-cache TTL (Cache-Control s-maxage=1, per RFC 9111) with request coalescing in front of an endpoint taking 5,000 requests per second, and origin sees roughly one request per second per cache node, a 99.98 percent reduction. Adding stale-while-revalidate (RFC 5861) removes the latency spike at expiry, because the edge answers from the stale copy while a single background fetch refreshes it.
The short verdict by workload:
The request path is identical for both. The edge computes a cache key, looks it up, and serves a HIT. On a MISS it fetches from origin, ideally through an origin shield so that many edges collapse into one upstream request, then stores the response if its headers allow and returns it. Static and dynamic content diverge on three variables only: TTL length, cache key width, and how invalidation happens.
Images, video segments, stylesheets, JavaScript bundles, installers and archives rarely change after publication. The correct pattern is a content hash in the filename plus Cache-Control: public, max-age=31536000, immutable. A new release then ships under a new URL instead of relying on a purge. At this point the hit ratio depends mostly on long-tail popularity and cache capacity, not on TTL tuning. Well-run static zones commonly sit above 95 percent.
Personalized pages, dashboards, prices, scores and search results change per second or per user. Most of these responses are still shareable for a short window or across a group of users. The engineering work is finding that window and that group, then encoding both in headers and cache rules. Edge-Side Includes (ESI) or edge logic then assemble the cacheable shell with the small user-specific fragment fetched from origin.
Dynamic caching is the practice of caching frequently changing HTTP responses at the CDN edge for very short, deliberately chosen periods, typically 1 to 60 seconds. It is paired with request coalescing and stale-serving directives, so origin sees a bounded request rate regardless of traffic. It trades a small, known staleness window for large reductions in origin load and tail latency.
Origin load under micro-caching is roughly cache nodes divided by TTL, independent of client traffic. Take 40 edge nodes, no shield and a 1-second TTL: origin peaks near 40 requests per second whether clients send 500 or 50,000. Put an origin shield in front and the figure drops toward 1 per shield node. In nginx, the same pattern is a short proxy_cache_valid for 200 responses, proxy_cache_lock on so concurrent misses wait for one fetch, and proxy_cache_use_stale updating with proxy_cache_background_update on.
A header such as Cache-Control: public, s-maxage=5, stale-while-revalidate=30, stale-if-error=300 tells a shared cache three things:
The second directive removes the p99 spike at expiry. The third turns an origin outage into staleness instead of 5xx errors. Support varies by CDN, so confirm both directives in vendor documentation before relying on them.
The cache key decides correctness. Too narrow and users see each other's data. Too wide and the hit ratio collapses. Build keys from the smallest set of inputs that actually change the response: path, a normalized and allow-listed set of query parameters, and at most a few low-cardinality dimensions such as device class, country, language or logged-in versus anonymous.
These rules are also where location-, device- and content-type-based cache durations belong. A product page can carry a 30-second TTL while its price fragment carries 2 seconds.
Dynamic content delivery for truly uncacheable responses (checkout, authenticated writes, per-user API calls) still benefits from a CDN through dynamic acceleration. The edge terminates TCP and TLS near the user, reuses warm long-haul connections to origin, and routes over the best available path. It reduces the round trips a request pays, without storing anything.
The arithmetic, as an estimate. A user 150 ms of round trip from origin opening a fresh TCP plus TLS 1.3 connection pays about 3 round trips before the first byte: roughly 450 ms. The same user 20 ms from an edge holding a pooled origin connection pays about 2 × 20 + 150 = 190 ms. That saves around 260 ms on the first request. Edge compute extends the idea by moving token validation, A/B assignment and fragment assembly to the edge, which removes the origin round trip entirely for those steps.
| Content | Edge TTL | Cache key | Invalidation | Main risk |
|---|---|---|---|---|
| Fingerprinted JS, CSS, images | 1 year, immutable | Path only | New URL per release | Unversioned file names |
| Video segments, installers, patches | Days to 1 year | Path, ignore query | Purge or new path | Cold-cache origin floods at release |
| Anonymous HTML | 5 to 60 s plus stale-while-revalidate | Path, normalized query, language | Tag-based purge | Caching a Set-Cookie response |
| Public API reads (prices, scores) | 1 to 5 s | Path, allow-listed params | TTL expiry | Unkeyed params returning wrong data |
| Logged-in pages | Shell 30 to 300 s, fragment 0 | Path plus segment | Tag-based purge | Cross-user data leaks |
| Cart, checkout, writes | None (private, no-store) | Not applicable | Not applicable | Accidentally cached POST or auth responses |
Only carts, checkout and writes are truly uncacheable; everything else is a choice of TTL and key width.
| Failure | How it shows up | How to confirm |
|---|---|---|
| Personalized response cached for everyone | Users report seeing another account's name or cart | Any response with Set-Cookie or Authorization and an Age above 0 |
| Cache poisoning via unkeyed headers | Broken redirects or wrong host in cached HTML | Vary a forwarded header the origin reflects; check whether the cached copy changes |
| Key cardinality explosion | Hit ratio on dynamic paths below 30 percent despite heavy traffic | Count unique keys per path; look for Vary: User-Agent or raw tracking params |
| Thundering herd at expiry | Origin CPU sawtooth aligned to the TTL period | Origin requests per second per URL spike every TTL seconds; coalescing is off |
| Purge not propagating | Old price visible in one region only | Compare Age and ETag from several regions after a purge |
Cross-user leaks are the failure that matters most, because the rest cost performance while this one costs a security incident.
A cached response skips every origin-side check. Authorization therefore has to live in the cache key or at the edge: signed URLs or tokens validated before lookup, and private, no-store on anything tied to a session. TLS on both legs, plus the DDoS mitigation and bot management your CDN or security vendor provides, protect the dynamic tier. Bots love uncached search and login endpoints because every request reaches origin.
Offload is where the money is. Every point of hit ratio removes origin compute and egress. For e-commerce, micro-cached listing pages keep browsing responsive during sales peaks. Media and gaming push most of their bytes as static segments, builds and patches, where cache warm-up before a known release prevents the cold-cache flood. Predictive and machine-learning TTL tuning gets marketed heavily. Explicit TTLs plus warm-up before known events deliver most of the value without the opacity.
Splitting tiers across providers is a common pattern. BlazingCDN is built for the static side of the decision table: high-volume video, installers, game builds and images, with origin shield, request coalescing and an average cache hit ratio above 96 percent. It can run as a second CDN behind DNS with a weighted traffic split, so heavy static bytes move while dynamic acceleration and security stay with your existing stack.
Yes, a CDN can cache dynamic content when the response is shareable for a short window or across a group of users. Typical setups micro-cache anonymous HTML and public API reads for 1 to 60 seconds and cache personalized pages by segment. Truly per-user responses such as carts and checkout stay uncached and rely on dynamic acceleration instead.
Start with 1 to 5 seconds for prices, scores and inventory, and 30 to 60 seconds for anonymous HTML. Origin load under micro-caching scales with cache nodes divided by TTL, so even 1 second removes most traffic at high request rates. Raise the TTL only after confirming the business tolerates that staleness window.
It works on CDNs that implement RFC 5861 and is especially valuable for dynamic content. The edge serves the expired copy instantly while one background request refreshes it, which removes latency spikes at expiry. Support and exact semantics differ between providers, so verify behavior in vendor documentation and test it before depending on it.
Cache personalized content by segment, never by user identity. Key on low-cardinality values such as plan, region or language, cache the page shell, and fetch user-specific fragments separately. Mark any response that sets cookies or depends on a session as private or no-store, and alert when such a response is served with an Age header above zero.
Dynamic caching is safe for public, idempotent GET responses whose cache key includes every parameter that changes the output. Allow-list query parameters, normalize their order, and never cache responses to authenticated or write requests. Unkeyed parameters are the common bug: two clients send different filters and both receive whichever response was cached first.
Dynamic caching stores frequently changing responses briefly at the edge, while dynamic content delivery accelerates responses that cannot be stored at all. Delivery relies on TLS termination near the user, warm pooled connections to origin and path optimization, typically saving a few hundred milliseconds on long-distance first requests. Most production setups combine both.
Export one day of edge or origin logs and bucket every request into the six rows of the decision table above. Then compute what fraction of origin requests come from anonymous HTML and public API reads. That fraction is your micro-caching opportunity. Enable a 1-second TTL with request coalescing on the single busiest endpoint, and compare origin requests per second and p99 latency before and after. Run the Set-Cookie alert first.
If the exercise shows that most of your bytes sit in the static rows, the BlazingCDN features for static content caching list origin shield, request coalescing, purge, cache warm-up through the API and Prometheus metrics on every plan.

Heavy traffic.
Light bill.
The CDN for video and large traffic
Learn
The precise answer to what is HDR video: high dynamic range video is video encoded with 10-bit or higher samples, ITU-R ...
Pricing - Pricing & Costs
DigitalOcean CDN (Spaces CDN) is included in the $5 per month Spaces subscription. According to DigitalOcean list ...